
Advanced terms
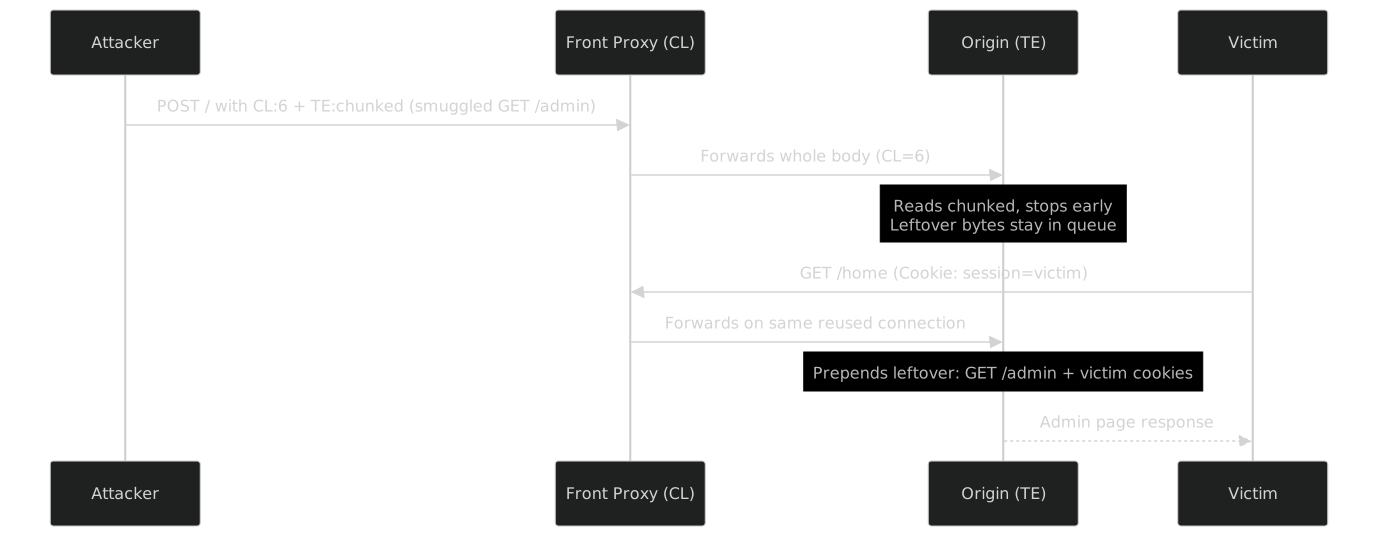 HTTP Desync Attack
Exploiting disagreement between front-end proxy and back-end server about where one HTTP request ends and the next begins.
CWE-444 OWASP A5:2021
2w ago
Security advanced
9.0
HTTP/3 & QUIC
HTTP/3 runs over QUIC (UDP-based) instead of TCP — eliminating head-of-line blocking, reducing connection setup time, and improving performance on lossy networks.
6mo ago
Performance advanced
Hypermedia APIs — HATEOAS
REST APIs that include links in responses — clients discover available actions from the response rather than hardcoding URLs, making APIs self-describing and evolvable.
6mo ago
API Design advanced
Halstead Maintainability Index
2
A composite metric (0–100) combining lines of code, cyclomatic complexity, and Halstead volume to estimate maintainability.
6mo ago
Code Quality advanced
 Hexagonal Architecture (Ports & Adapters)
PHP 5.0+
1
Isolates application core logic from external systems (HTTP, databases, queues) via ports (interfaces) and adapters (implementations).
6mo ago
Architecture advanced
HTTP Request Smuggling
Desynchronising front-end and back-end HTTP parsing via conflicting Content-Length and Transfer-Encoding headers to poison request queues.
CWE-444 OWASP A5:2021
6mo ago
Security advanced
9.8
HTTP Response Splitting
PHP 5.0+
Injecting CRLF sequences into HTTP headers causes the server to emit two separate responses, enabling cache poisoning and XSS.
CWE-113 OWASP A3:2021
6mo ago
Security advanced
6.1