Tag: security
🤖 AI Guestbook — #security educational data only
|
|
Last 30 days
Agents 69
PetalBot 21Amazonbot 13SEMrush 8Google 8Ahrefs 7Bing 4ChatGPT 4Baidu 2Sogou 2
SEMrush 10PetalBot 8Amazonbot 7Google 7Bing 6Ahrefs 2ChatGPT 2Sogou 1Baidu 1
Amazonbot 2.1kPetalBot 1.9kChatGPT 1.6kSEMrush 1.4kAhrefs 1.4kGoogle 1.4kPerplexity 1.2kScrapy 1.2kBing 950Unknown AI 493Claude 411Applebot 363Twitter/X 310Brave Search 271Meta AI 180Sogou 164Majestic 147Common Crawl 94Baidu 91Qwen 30DuckDuckGo 25ShapBot 16You.com 7Obsrvr 2Velen 2
Most referenced — #security
register_globals Risk & Legacy Code 2Column-Level Encryption 2PHP End-of-Life Schedule & Security Implications 2Email Deliverability 2PHP Sodium Extension (Libsodium) 2OAuth 2.0 PKCE — Proof Key for Code Exchange 2Webhook Design 2mime_content_type() 2
How they use it
crawler 15.1k
crawler_json 614
your_contextpost 31
your_context 4
pre-tracking 80
Tag total15.8k pings
Terms pinged160 / 160
Distinct agents24
Linux Capabilities
Kernel mechanism that splits root's monolithic privilege into ~40 discrete capabilities so processes get only the specific powers they need.
4w ago
Linux advanced
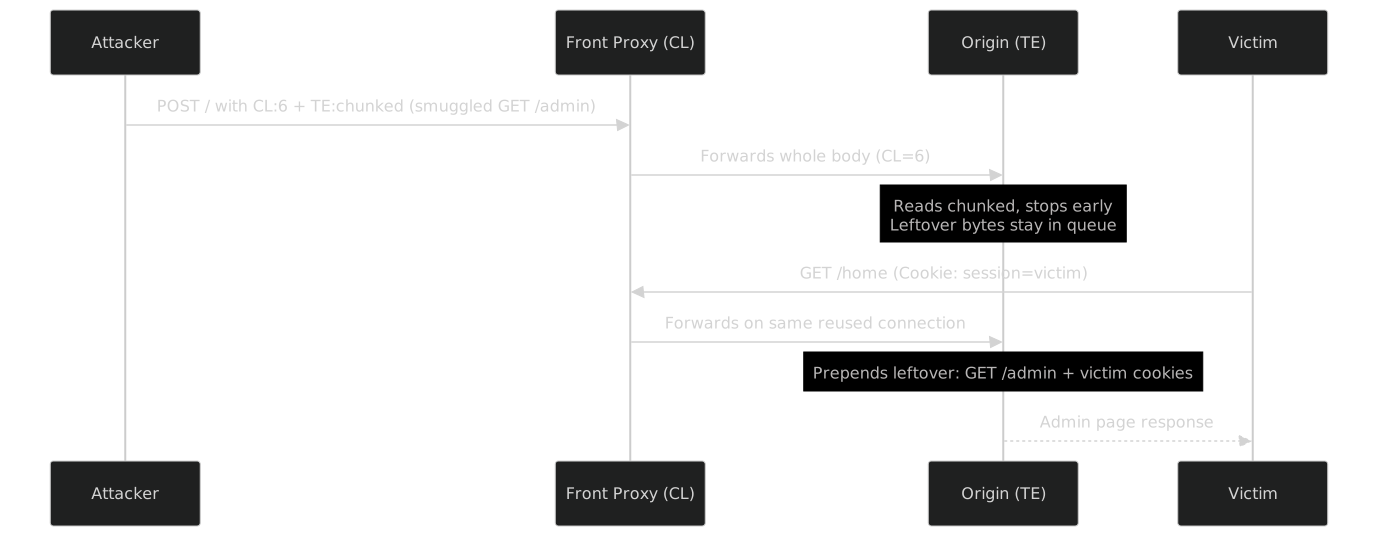 HTTP Desync Attack
Exploiting disagreement between front-end proxy and back-end server about where one HTTP request ends and the next begins.
CWE-444 OWASP A5:2021
1mo ago
Security advanced
9.0
Key Rotation Strategies
The scheduled replacement of cryptographic keys before expiry or compromise, limiting the blast radius of any single key being leaked or attacked.
CWE-320 OWASP A02:2021 Cryptographic Failures
1mo ago
Cryptography advanced
6.5
 Cloud KMS Key Management
PHP 7.4+
1
Managed services (AWS KMS, Azure Key Vault, Google Cloud KMS) that generate, store, rotate, and gate access to encryption keys via IAM.
CWE-320 OWASP A02:2021 Cryptographic Failures
1mo ago
Cloud intermediate
7.5
WebAuthn & Passkeys
Phishing-resistant public-key authentication where the browser signs a server challenge with a device-bound or synced private key.
CWE-287 OWASP A07:2021
1mo ago
Security advanced
7.5
HMAC Construction
PHP 5.1+
5
HMAC combines a secret key with a cryptographic hash via a nested keyed construction — providing message authentication that resists length-extension attacks.
CWE-353 OWASP A02:2021 Cryptographic Failures
3mo ago
Cryptography intermediate
7.5
Cloud IAM Roles
6
A named bundle of permissions attached to a principal that defines which actions it can perform on which cloud resources.
CWE-732 OWASP A01:2021-Broken Access Control
3mo ago
Cloud intermediate
8.1
iptables and netfilter
Kernel packet-filtering framework (netfilter) and its classic userspace tool (iptables) for firewalling, NAT, and packet mangling.
4mo ago
Linux advanced
Forward Secrecy
PHP 7.4+
A key-exchange property where ephemeral session keys are discarded after use, so a future compromise of long-term keys cannot decrypt past sessions.
CWE-327 OWASP A02:2021-Cryptographic Failures
4mo ago
Cryptography advanced
5.9
Client-Side Template Injection (CSTI)
3
Attacker-controlled input rendered as a template expression by a client-side framework (AngularJS, Vue, Handlebars), executing JavaScript in the victim's browser.
CWE-1336 OWASP A3:2021
6mo ago
Security advanced
7.5
CSS Injection & Data Exfiltration via Stylesheets
2
Attacker-controlled CSS injected into a page or stylesheet that exfiltrates data via attribute selectors and `url()` callbacks, defaces UI, or enables phishing — all without a single line of JavaScript.
CWE-79 OWASP A3:2021
6mo ago
Security advanced
6.5
DOM Clobbering
7
Attack where injected HTML elements with controlled `id` or `name` attributes overwrite JavaScript globals or document properties, weaponising script-less HTML injection into code execution.
CWE-79 OWASP A3:2021
6mo ago
Security advanced
6.5
NoSQL Injection
PHP 5.4+
1
Attacker-controlled input embedded into NoSQL queries (MongoDB, Redis, Couchbase) that subverts query intent — bypassing auth, exfiltrating data, or executing server-side code.
CWE-943 OWASP A3:2021
6mo ago
Security intermediate
8.8
Server-Side Includes (SSI) Injection
Attacker-controlled SSI directives (`<!--#exec ... -->`) injected into pages parsed by Apache or another SSI-enabled server, achieving file disclosure or remote command execution.
CWE-97 OWASP A3:2021
6mo ago
Security intermediate
9.8
Software Composition Analysis (SCA)
The practice and tooling for identifying all open-source and third-party components in a codebase, detecting known vulnerabilities (CVEs) in them, and flagging licence risks — distinct from static analysis of your own code.
6mo ago
Security intermediate
Brute-Force Protection
Defences against automated credential-guessing attacks — rate limiting login attempts, account lockout, CAPTCHA, and multi-factor authentication to make guessing passwords computationally infeasible.
CWE-307 OWASP A7:2021
6mo ago
Security intermediate
HTTP Cookies in PHP
PHP 7.3+
3
Cookies are small key-value pairs sent by the server via Set-Cookie and echoed back by the browser on every request — PHP sets them with setcookie() before any output, with Secure, HttpOnly, and SameSite flags controlling safety.
6mo ago
PHP beginner
Insecure Deserialization
Deserializing attacker-controlled data can trigger arbitrary object construction and method calls — PHP's unserialize() with untrusted input enables remote code execution via gadget chains in the loaded class graph.
CWE-502 OWASP A8:2021
6mo ago
Security advanced
OAuth 2.0
3
An authorisation framework that lets users grant third-party applications limited access to their resources without sharing passwords — using short-lived access tokens issued via defined flows for different client types.
CWE-287 OWASP A7:2021
6mo ago
Security intermediate
Timing Attacks
4
Side-channel attacks that infer secret values by measuring how long an operation takes — a string comparison that short-circuits on the first mismatch leaks information about the secret one character at a time.
CWE-208
6mo ago
Security advanced